What Does a Security Operations Center Analyst Do?
 Gregory Evans
A security operations center analyst is the frontline defender of an organization’s digital infrastructure. They monitor network traffic, detect cyber threats, and respond to security incidents in real time. If a breach happens, a SOC analyst is usually the first person to catch it and take action.
Think of it like being a security guard for a computer network. Instead of watching cameras in a building, you’re watching alerts, logs, and system activity across an entire organization. When something suspicious pops up, you investigate it, figure out how serious it is, and move fast to stop it before real damage happens.
If you’re curious about a career protecting networks and want to understand what this role actually looks like day to day, you’re in the right place. Let’s break down what a SOC analyst does, what the job demands, and whether it’s the right path for you.
The Core Responsibilities of a SOC Analyst
A security operations center analyst has a few main jobs that repeat throughout every shift.
Threat Detection and Monitoring
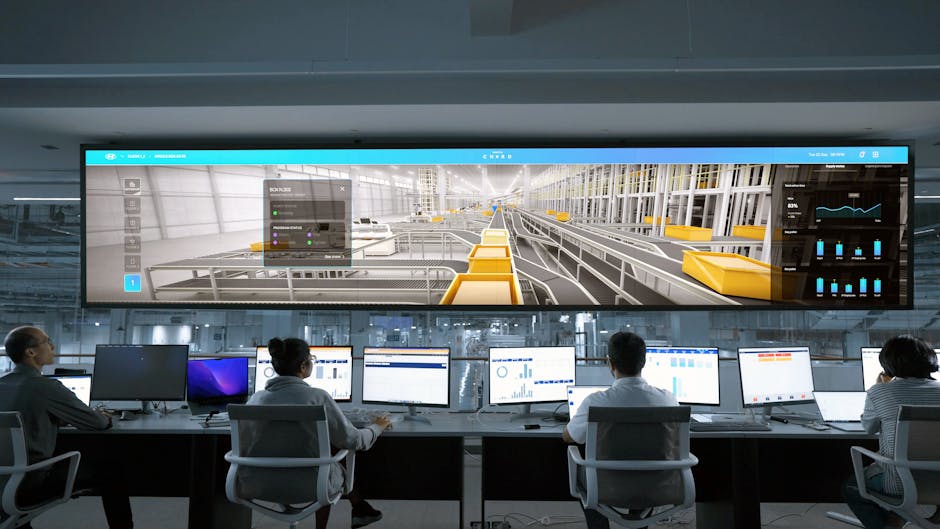
Your primary job is to watch. SOC analysts sit at security monitoring dashboards and review logs, alerts, and network traffic all day. You’re looking for anything that doesn’t belong: unusual login attempts, unexpected data transfers, malware signatures, or suspicious connection patterns.
This isn’t a guessing game. You use security tools like SIEM (Security Information and Event Management) platforms to aggregate and visualize activity across the entire network. The tools flag potential threats, and you investigate whether they’re real problems or false alarms.
Incident Response and Triage
When a security alert fires, you’re the first responder. You collect information about what happened, categorize the severity of the incident, and decide what to do next. Is this a minor misconfiguration? A real attack in progress? You triage incidents by urgency so the most dangerous ones get handled first.
Containment and Isolation
If a threat is confirmed, you take action immediately. This might mean disconnecting a compromised computer from the network, terminating suspicious processes, resetting compromised credentials, or blocking malicious IP addresses. The goal is to stop the threat from spreading before it affects more systems or data.
Analysis and Documentation
After you contain an incident, you dig deeper. You analyze logs to understand how the attack happened, what systems were touched, and what data might have been accessed. You document everything so other team members, security leadership, and sometimes regulators can understand the full picture of what went wrong.
If you’re interested in learning hands-on skills for incident response and threat analysis, National Cyber Security Training Academy offers training on SOC tools and real-world detection scenarios.
What SOC Analysts Actually Do During a Shift
Here’s what a realistic day looks like.
Morning Briefing
Your shift starts with a handover from the previous team. They brief you on any ongoing incidents, alerts that need follow-up, or new threats they noticed. Then you log into your monitoring dashboards and scan overnight activity.
Alert Investigation
Alerts come in constantly. Some are noise. A user locked out after failed login attempts? Probably normal. A mass file encryption event on a server? That’s worth investigating. You gather context: who was affected, what systems, what time, what changed recently.
Escalation and Handoff
Not every threat is something you handle alone. If you find evidence of a real attack, you escalate it to incident response specialists or threat hunters who dig deeper. You write a clear summary so they understand what you found and why it matters.
Tool and Process Updates
SOC teams are always refining how they work. You might contribute feedback on tuning alert rules to catch real threats while reducing false positives. You might help update playbooks (step-by-step instructions for handling common incidents) based on what you’re seeing.
Continuous Learning
Threats change constantly. Part of your job is staying sharp on new attack techniques, new vulnerabilities, and updates to your organization’s systems. Many SOC analysts spend some shift time reading threat intelligence, taking online training, or studying for certifications.
Key Skills You Need as a SOC Analyst
Technical Skills
- Networking fundamentals: TCP/IP, DNS, HTTP, firewalls, proxies
- Operating systems: Windows and Linux administration basics
- Log analysis: Reading and interpreting SIEM logs, event viewers, system logs
- Malware analysis: Recognizing suspicious file behavior and indicators of compromise
- Security tools: Proficiency with endpoint detection, intrusion detection systems, and log aggregation platforms
- Command line: Comfort using bash, PowerShell, or similar tools to query systems
Soft Skills
- Attention to detail: Missing one small sign in logs could mean missing an attack
- Stress management: Incident response happens fast and sometimes happens all at once
- Communication: You need to explain technical findings to non-technical executives and other teams
- Problem-solving: Incidents rarely fit a textbook scenario. You improvise and adapt
- Teamwork: SOC analysts work in round-the-clock shifts with security engineers, threat hunters, and management
How to Start a Career as a SOC Analyst

Most SOC analyst jobs expect you to know the basics of networking and operating systems before you start. You don’t need years of experience, but you do need foundational knowledge.
The typical path is to start with CompTIA Security+ or similar entry-level certification, then get hands-on practice in a SIEM tool, and apply for SOC analyst or “Security Analyst” roles at mid-sized and larger companies.
Many employers also value certifications like the CompTIA CySA+ (Certified Security Analyst) or specialized training in security incident response. The key is combining classroom learning with real lab experience so you understand how to use the tools and think like an attacker.
If you want structured training that covers both foundational cybersecurity and applied incident response skills, National Cyber Security Training Academy teaches the concepts and tools you’ll use in a real SOC environment.
Related: What Does a Cybersecurity Consultant Do? A Real Guide
Growth and Career Progression
SOC analyst is not a dead-end role. It’s a launching pad.
Related: What Does a Cybersecurity Specialist Do? Career Guide
After a few years detecting incidents, many analysts move into senior analyst roles where they mentor newer team members and handle more complex investigations. Others move into threat hunting, where you proactively search networks for signs of compromise rather than waiting for alerts to fire.
Some transition into incident response management, where you lead teams through major breaches. Others specialize in malware analysis, threat intelligence, or security engineering.
The role gives you real-world exposure to how attackers work and how organizations defend themselves. That knowledge is valuable across every corner of cybersecurity and even in adjacent fields like risk management or compliance.
Is SOC Analyst Work Right for You?
This job is not for everyone, and that’s okay to acknowledge upfront.
You should pursue this role if you’re naturally curious about how systems work, you stay calm under pressure, and you enjoy pattern recognition and problem-solving. You should also be comfortable with the fact that SOC teams often run 24/7 shifts, so you might work nights, weekends, or odd hours early in your career.
The pay is solid and the demand is high. The work is never boring. But you will see the worst of the internet and spend a lot of time chasing false alarms before you get really good at filtering the noise.
If that sounds like something you could be good at and enjoy, this is one of the best entry points into professional cybersecurity. You gain skills, earn certifications, build a track record of incident handling, and open doors to specialized roles down the road.
Frequently Asked Questions
Do I need a degree to become a SOC analyst?
No. Most employers care more about certifications, technical skills, and hands-on experience than a college degree. CompTIA Security+ and practical experience with SIEM tools, networking, and Windows/Linux will get you hired faster than a degree alone. That said, a degree in computer science or IT can help you land your first role if you don’t have prior experience yet.
What tools do SOC analysts use most?
SIEM platforms like Splunk, Elastic, or ArcSight are core. You’ll also work with endpoint detection and response tools, firewall logs, intrusion detection systems, and threat intelligence feeds. The exact tools vary by company, but if you understand the concepts behind log analysis and threat detection, you can learn any new tool quickly.
How stressful is a SOC analyst job?
It depends on the organization and the severity of incidents they face. Some SOC teams handle mostly routine alerts and tuning. Others are in constant incident response mode. The best way to manage stress is to stay organized, communicate clearly with your team, and take time to learn so you feel confident making decisions under pressure.
What’s the difference between a SOC analyst and a threat hunter?
A SOC analyst responds to alerts and known incidents. A threat hunter proactively searches the network for signs of compromise that security tools may have missed. Threat hunters typically need more advanced skills and experience, which is why many people start as SOC analysts and move into threat hunting after a few years.